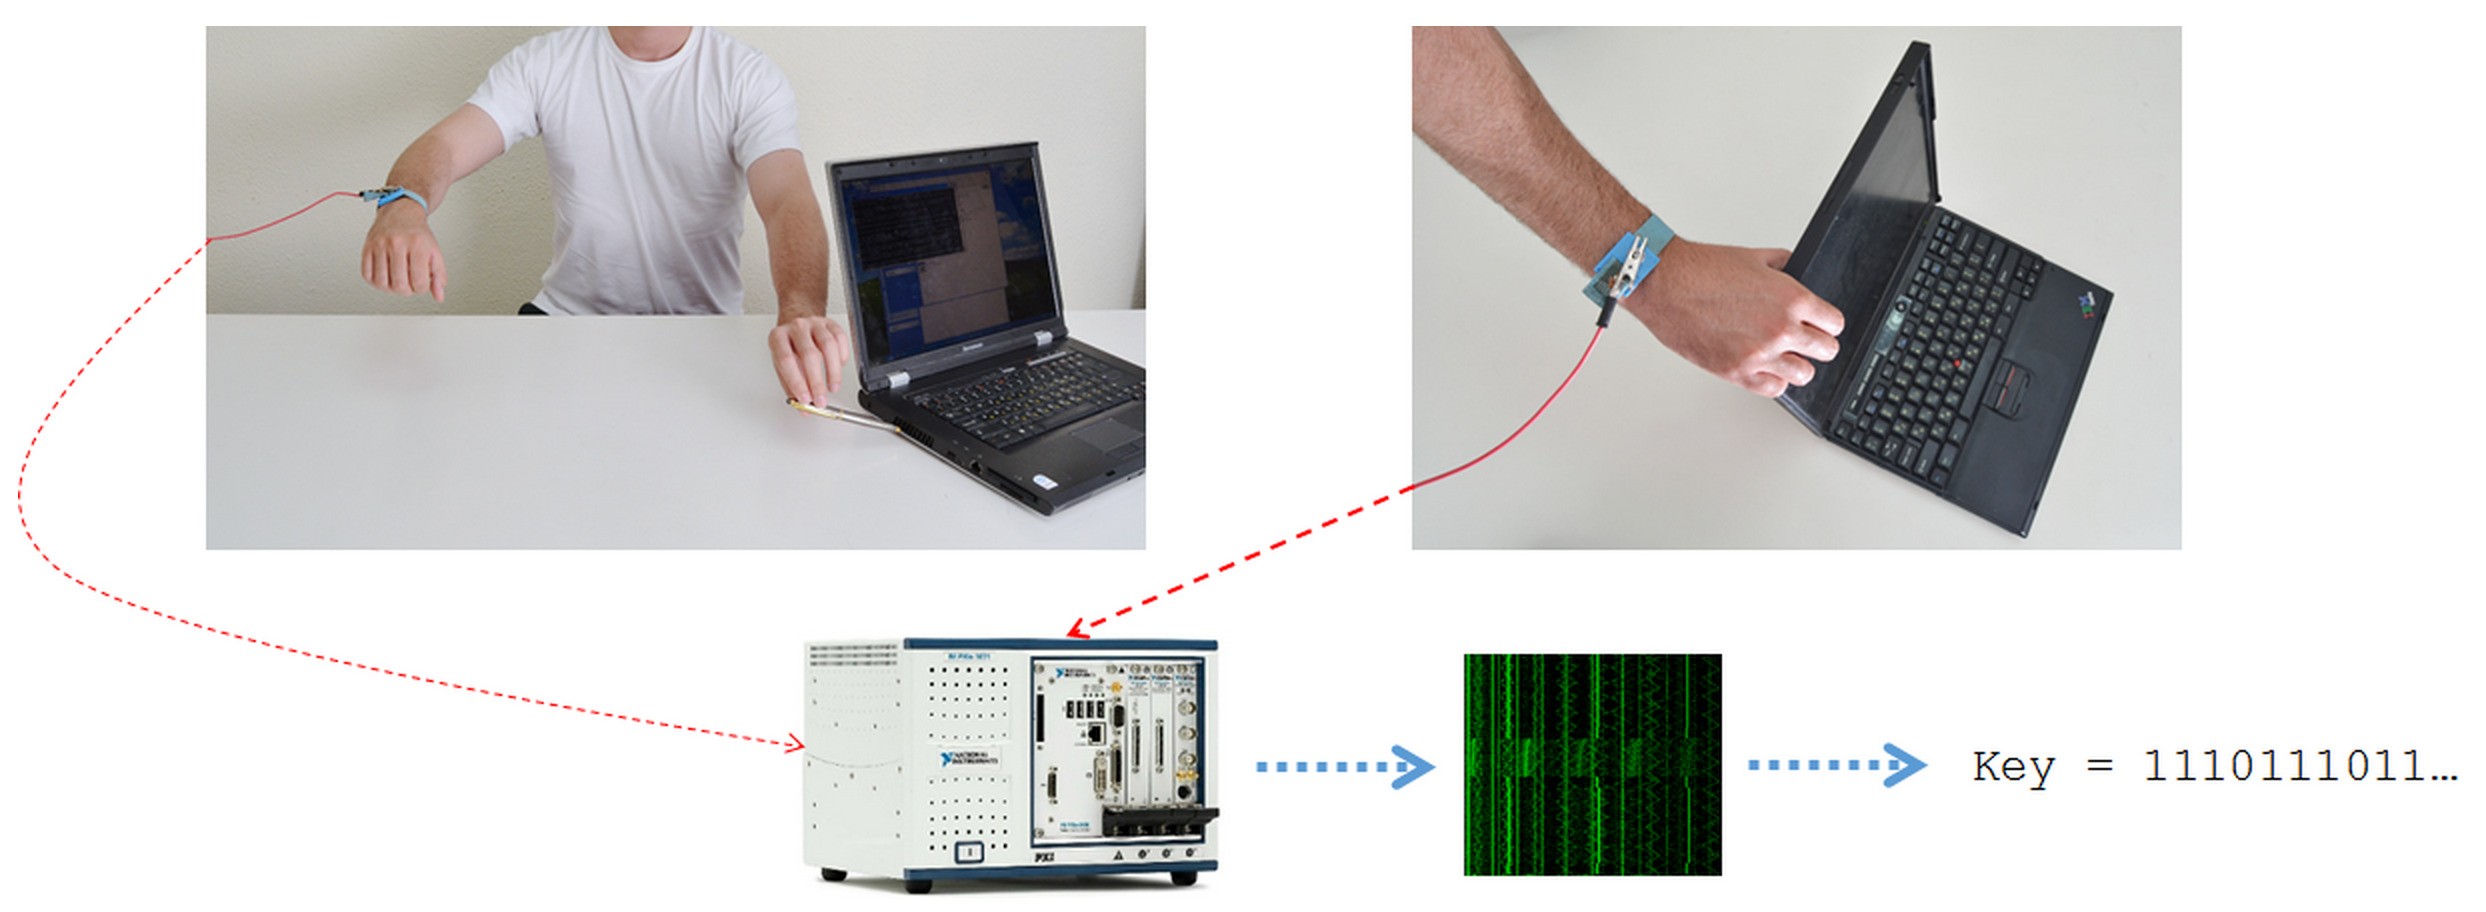
[caption id="attachment_1087" align="aligncenter" width="640"]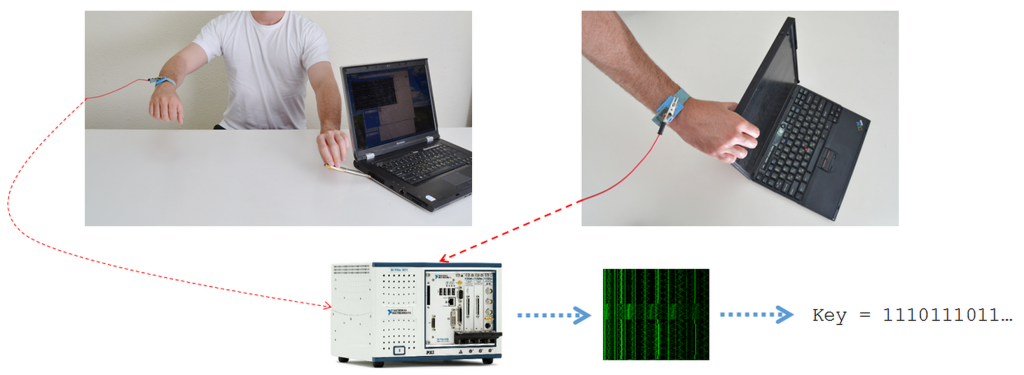 steal encryption keys with touching laptops[/caption] Hackers around the globe have found an out of box idea of stealing data from computer with just a simple touch over the laptop. Eran Tromer a security researcher at Tel Aviv University found an electrical key which is sufficient enough to steal away all the encryption keys.Most of the attacks use a ground zero potential which fluctuates in a computer dependent way. The security researcher wrote in an online paper that he can measure the signal with just a wire attached on his hand. The hand touches the metal part of the laptop which continuously generates different low potential signals. Not only this but also the remote end of the USB, Ethernet, or VGA cables can be used to measure the signal. The security researchers claim that they are able to steal more than thousands of encryption keys with a simple touch over the metal part and measuring the low potential signals. The encryption keys are mostly used at the time of creating passwords, credit and debit cards. The author claims that most of the time when a CPU tries to capture the encryption keys, different signals is released. So a it becomes easy for the attacker to make a drive by attack, just a little bit of planning is required.
Encryption keys and frequency signals
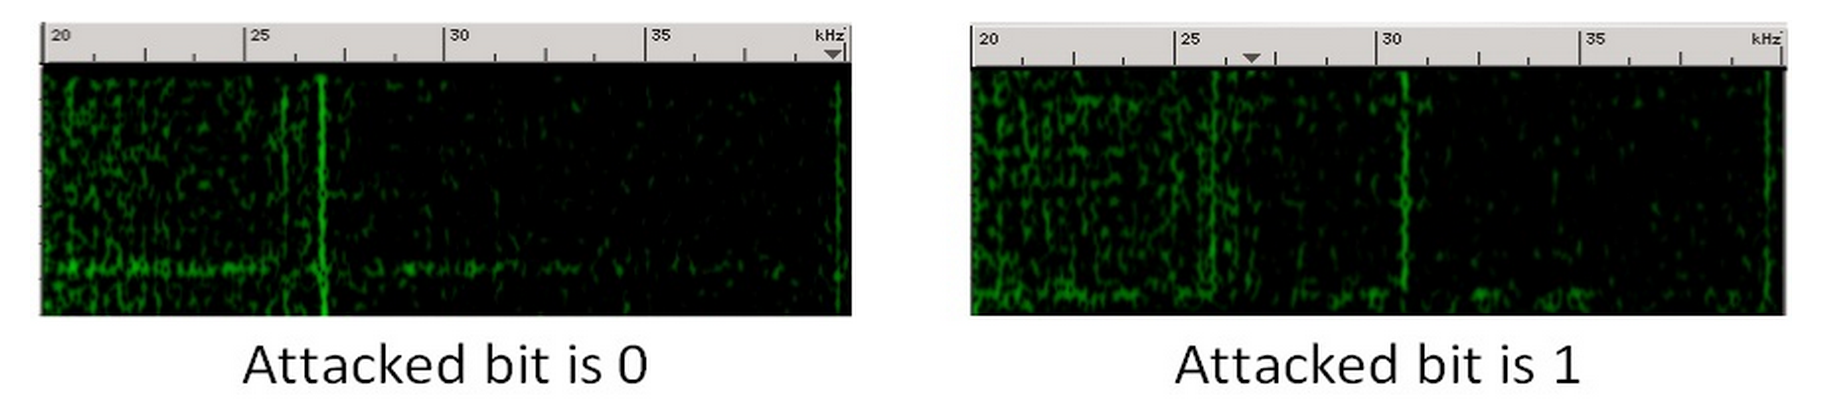
Although the attack is done quickly still it takes few seconds to measure the medium frequency signals (2 MHz) and low-frequency signals (2 KHz). Eran gave some impressive results by measuring these signals. First one is GnuPG can be used in distinguishing between the RSA secret keys. Moreover cipher text can be used with a mix up of changing potentials in extracting the encryption keys. Here is an image which captures the bit which is passed through the potential signal. [caption id="attachment_1088" align="aligncenter" width="640"]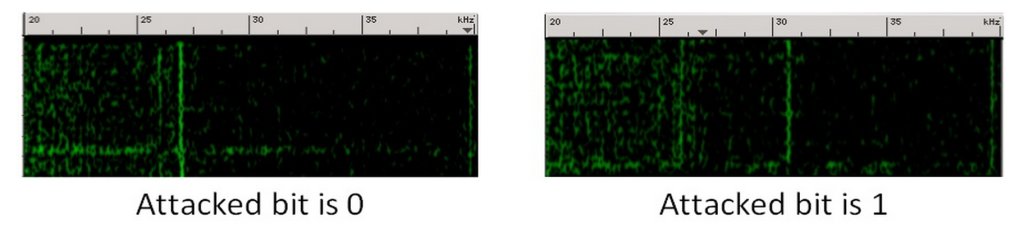 Capturing the bit from the potential signal[/caption] When Eran was questioned about the extent of usage of this attack, he said that, he doesn't think that the attackers are aware enough about how to make this attack.
Also See
[caption id="attachment_1034" align="alignleft" width="150"] Exploiting YouTube as network injectors[/caption]