[caption id="attachment_1035" align="aligncenter" width="624"]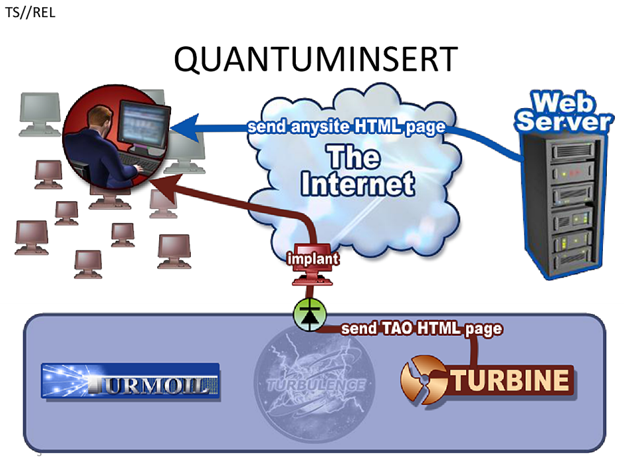 Quantuminsert a system used for network injection[/caption] Google's YouTube and Microsoft's live services today have become a major target of commercial network injector. CloudSheild Technologies a US department of Defense contractor is selling network injection appliances to Oman and Turkmenistan. According to the HackTeam and FinFisher report YouTube is targeted most for malware implantation.
Exploiting YouTube as surveillance tool
Taking the benefits of the security weakness of YouTube, vendors from around the globe have started selling software's at a large-scale. The unencrypted streaming of YouTube allows hackers to use it as a spying tool. Below is an image which clearly illustrates the unencrypted streaming of YouTube. [caption id="attachment_1034" align="aligncenter" width="609"] Exploiting YouTube as network injector[/caption] A research was performed by Hacking Team of Citizen Lab. The Hacking Team used network injector which monitored HTTP connections and was used in backdoor implantation. Here is a screenshot of network injection appliance used by Hacking Team. [caption id="attachment_1033" align="aligncenter" width="611"]
 Network injection appliance[/caption] The basic idea behind Network injector is that they automatically identify the targeted device and implant the malware according the software rules. Network injector exploit YouTube by injecting malicious HTML-Flash into the videos. The above method requires users to update the flash player.
Step by step guidance
- Open up the Network injection GUI and select the target and its name.
- On the ISP's RADIUS record trace the target's specific stream.
- Wait for a while till the traffic is identified and it is redirected to network injection appliance.
- Now the video is blocked temporarily and malicious flash is injected.
- If the network injector are successfully able to inject the flash, the browser will pop up a message of flash player update. If the target device accepts it, malware and backdoor implantation would start.
Prevention from Network injector
Network injector work with assuming that most of streaming websites do not use encrypted traffic data. Thus website service providers are requested to serve all there data over TLS (Transport Layer Security). The use of HTTP strict transport security and pinning is also recommended which could mitigate the effect. A plugin named HTTP Nowhere claims that it only allows encrypted traffic, this could help small website owners to prevent their websites from network injector.
More To Read
[caption id="attachment_913" align="alignleft" width="150"] Learn Ethical hacking[/caption] [caption id="attachment_779" align="alignleft" width="150"]
 Fake Googlebots used for DDOS attack[/caption]