[caption id="attachment_980" align="aligncenter" width="450"]
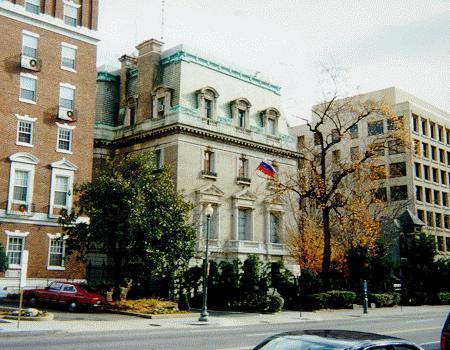
Malware attack made by hackers on Soviet Embassies[/caption]
Today, an unknown group of hackers attacked the former soviet embassies. A malware attack was made from UTC +4 time zones which belonged to Moscow. Embassies of countries like Ukraine, China, Poland and Germany have been targeted.
Symantec discovering the unknown malware attack
Security researchers from Symantec security firm discovered the malware attack. The firm said that the attack was made by nation-state for reconnaissance purpose. Most of the daily visited websites were targeted which were often visited by embassy staff. The malware attack was named as watering hole attack by the researchers. The malware was implanted by disguising the
shockwave installer. The plugin was spoofed up by the mysterious hackers which contained inbuilt .bat files.
The security researchers made a statement that if few high-profile malware were imparted then it would be easy to impart other malware also. High profile malwares include WPbot, Tavdig, Turla, Uroboros, Snake and Carbon was imparted in the shock-wave plugin. Among all WPbot was to be used to affect other computers.
"If the attackers deemed the victim of interest, it appears likely that a second back door Trojan with far greater capabilities was downloaded on to the victim's computer."
Also SEE:
[caption id="attachment_832" align="alignleft" width="150"]

Fake Facebook hacking software scam[/caption]
[caption id="attachment_971" align="alignleft" width="150"]

Cyber security one of the most highly paid jobs in world[/caption]