[caption id="attachment_985" align="aligncenter" width="660"]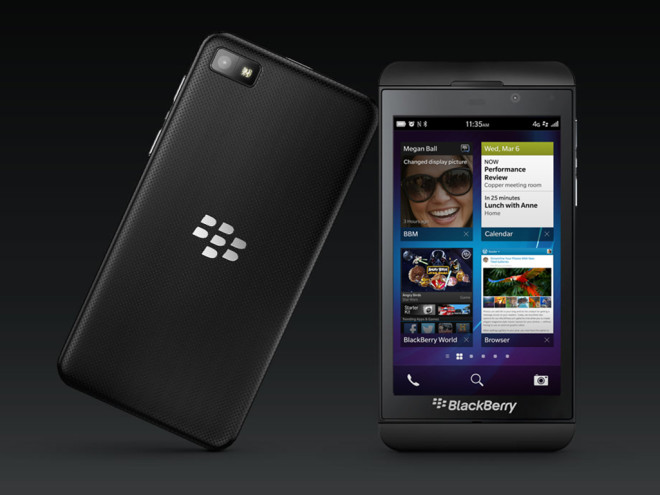 Blackberry Z10 found vulnerable to authentication bypass vulnerability[/caption] Blackberry's premium smartphone Z10 is found vulnerable to authentication bypass vulnerability. A hacker could easily steal user's data and can implant a malware inside the smartphone. Blackberry Z10 stores corporate and personal data separately. It is the only handset of Blackberry which enumerates encryption security. With Blackberry Z10 you can do ad-hoc file sharing with neighbouring devices over wireless networks. Modzero researchers in Switzerland had discovered vulnerability in this mechanism. They were able to bypass this authentication service.
Authentication bypass vulnerability found
Z10 gives you storage and access network service. This service is used for ad-hoc file exchange. The exchange of file usually happens between phone and network client. A file server named samba is deployed in between with which downloading and uploading of a file starts. Users need to explicitly enable Access using Wi-Fi if they want to publically access the fileservers through wireless networks. The authentication which was used as a security check point was being by passed. [caption id="attachment_986" align="aligncenter" width="680"] authentication bypass[/caption] Now the samba fileserver do not asks you any login id password and easily gives access to read and write the shared files. The authentication bypass vulnerability found can be easily exploited to implant malware inside the phone. The researchers discovered two methods for exploiting the authentication bypass vulnerability, but they said that the condition is not always reproducible and may take several attempts to show up. The authentication vulnerability bug is fixed by 2 different methods. First one is to access the fileservers with the help of wireless LAN interface. Second one is accessing the same fileservers with the help of USB cables. In the second method a TCP/IP connection is established in developer's mode. Blackberry has fixed the bug and has released patch for the authentication bypass vulnerability.
Also SEE:
[caption id="attachment_936" align="alignleft" width="150"] Facebook buys Private core solutions[/caption] [caption id="attachment_980" align="alignleft" width="150"]
 Malware attack made by hackers on Soviet Embassies[/caption]