[caption id="attachment_619" align="aligncenter" width="500"] Hack android device[/caption]
The most popularly used mobile operating system Android by Google is now having a serious vulnerability. Android vulnerability is found by a security firm Curesec in the Apps.
What is Android vulnerability?
Android vulnerability found is in its apps. Some of the latest and commonly used
android apps available on app store now can make
automatic phone calls to random numbers. This is because the
Android apps lack in necessary permissions.
This Android vulnerability was identified and
submitted to the Android developers last year by the
German security firm Curesec.
[caption id="attachment_618" align="aligncenter" width="640"]
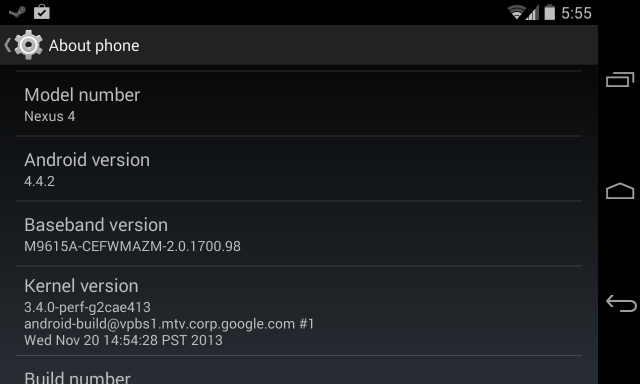
Google Android Vulnerability found[/caption]
Bug found will terminate outgoing calls and sends USSD
The android vulnerability would
allow apps to do terminate your ongoing phone calls and would sends USSD (Unstructured supplementary service data), Suplementary service SS and Man machine interface. The various
USSD codes are used to run the operator services and run mobile data packages.
Android versions which are Vulnerable
Orignally the
vulnerability was found in
Android 4.1 jelly bean but later when other Android versions were tested, they were also found vulnerable. In total there are
2 bugs found, one which is found in newer versions and second is found in older versions.
The first bug found is identified as
CVE-2013-6272. Android 4.1 jelly bean was first which was affected and later it continued in Android 4.2 and 4.3.
Android developer Google fixed this vulnerability in the latest version of Android Kit Kat 4.4.
Second security bug found is in the earlier
Android versions Ginger bird and ice cream sandwich. Only Android honey comb 3.0 is free from this vulnerability but the problem is that Honey comb 3.0 is only available for tablets.
Since the Android vulnerability is not found in the latest Kit Kat 4.4 version, users are advised to upgrade there smartphones to Kit Kat 4.4.
You might also like
[caption id="attachment_614" align="alignleft" width="150"]
Hack Facebook account with third party token[/caption]
[caption id="attachment_598" align="alignleft" width="150"]
Cyber Security Training[/caption]